
🚀 The Path to Mastery: A Roadmap to the Burp Suite Certified Practitioner (BSCP)
[!ABSTRACT] Demystifying the BSCP Journey Earning the Burp Suite Certified Practitioner (BSCP) designation validates your surgical skill: the ability to perform deep-dive analysis across diverse vulnerability classes, bypass defensive layers, and chain primitives under pressure. This roadmap is designed to guide you from foundational training to autonomous, practitioner-grade mastery.
🗺️ Visual Mind Map & Roadmap
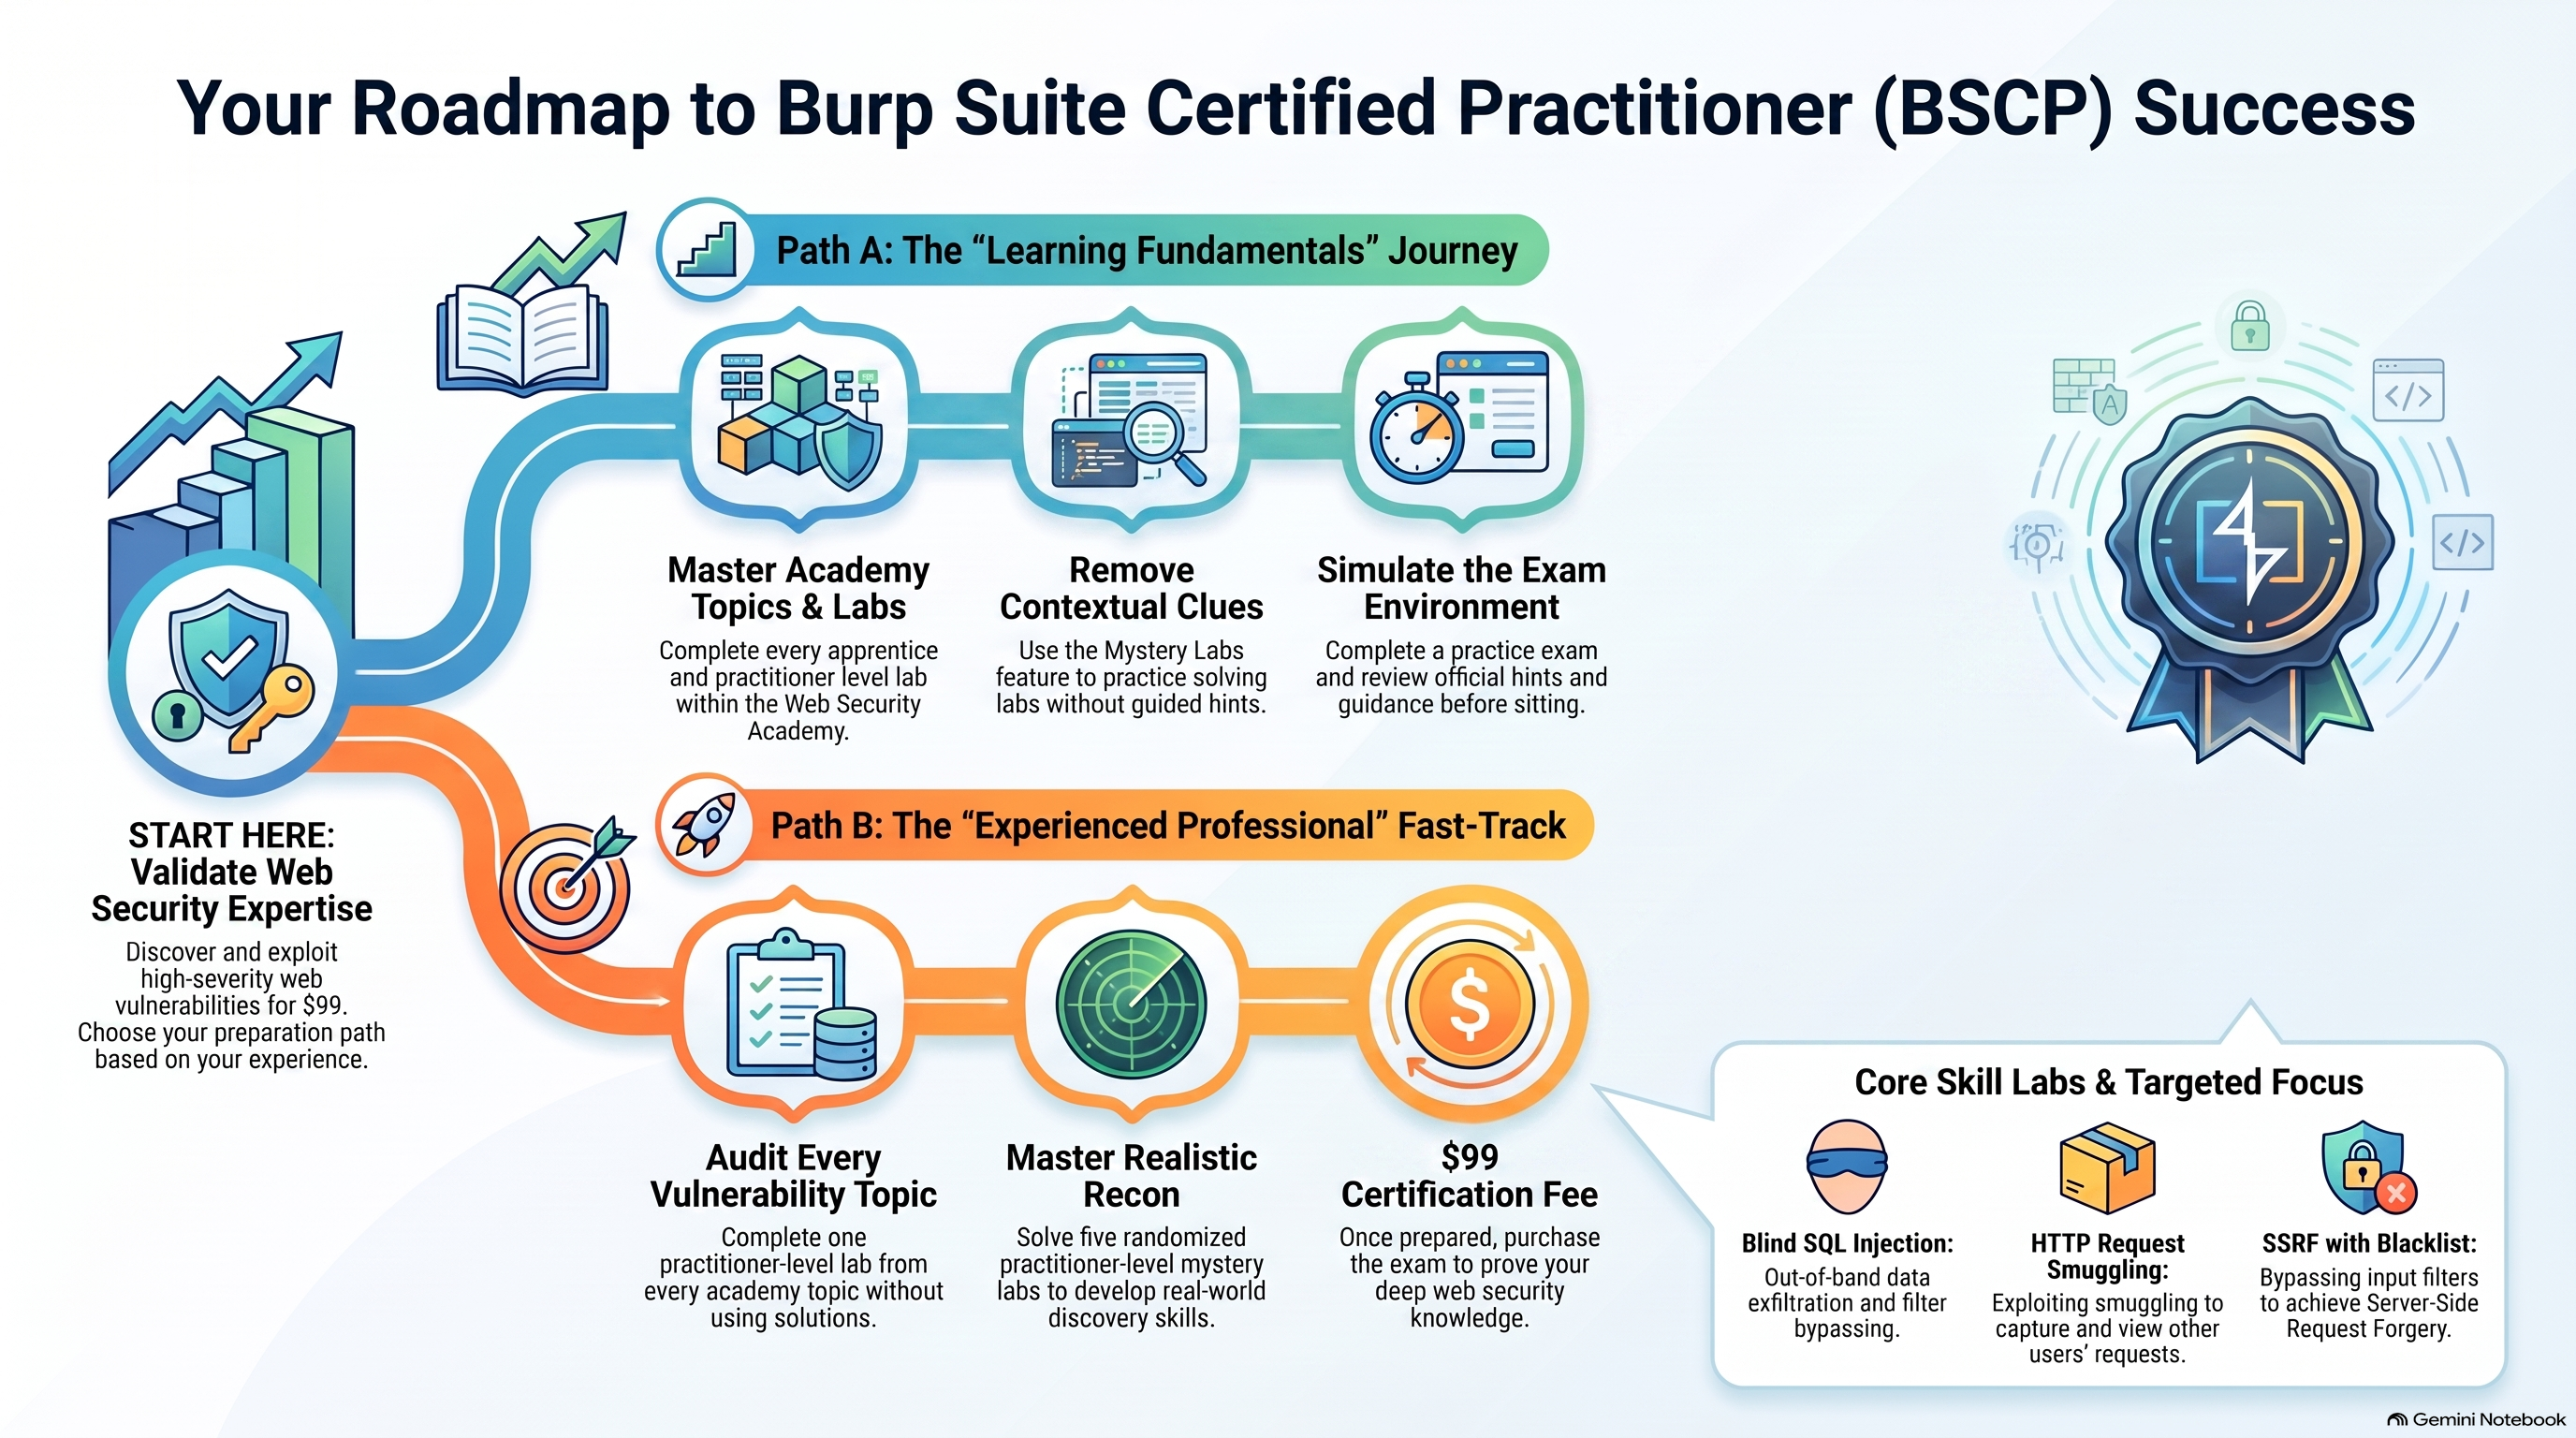
1. Choosing Your Starting Point: Tailored Learning Paths
| Learning the Fundamentals (Beginner Track) | Experienced Practitioner (Accelerated Track) |
|---|---|
| Step 1: The Foundation. Work through all Academy topics, completing every Apprentice and Practitioner-level lab. | Goal 1: Assess Range. Complete one practitioner-level lab from every single Academy topic without viewing the solutions. |
| Step 2: Contextual Reinforcement. Use the "Mystery Lab" feature at the end of each topic to solve challenges without cues. | Goal 2: Refresh Impact. Complete the Step 2 Prep Labs to practice turning vulnerabilities into high-severity exploits. |
| Step 3: Blind Discovery. Solve five randomized Mystery Labs across all topics to build raw recon skills. | Goal 3: Learn Mechanisms. Familiarize yourself with Academy-specific tools, such as the simulated exploit server and Collaborator. |
| Step 4: Full Simulation. Complete the Practice Exam to understand the two-hour format and environment. | Step 4: Final Validation. Pass the Practice Exam comfortably before purchasing the BSCP. |
| Step 5: Official Guidance. Study the exam hints and guidance for success-critical insights. | Constraint: If you cannot solve a lab without solutions, return to the learning materials for that topic. |
[!TIP] Pro-Tip for Beginners For those on the beginner path, completeness is your only metric. Do not attempt to bypass the fundamentals; you are ready for the mystery lab phase only after clearing every Apprentice and Practitioner level lab in the Web Security Academy.
2. The Mystery Lab Challenge: Developing "No-Context" Intuition
The "Mystery Lab" feature serves as the bridge between guided academic learning and the reality of a live engagement. In a standard lab, the title gives away the vulnerability. In the real world—and on the BSCP exam—there are no labels.
📋 Requirements for Experienced Learners:
- Sequential Success: Launch and solve five practitioner-level randomized challenges consecutively.
- Strict "No-Solutions" Discipline: Complete these challenges without hints or external walkthroughs.
- Environment Mastery:
- Utilize the standard test credentials (
wiener:peter) for baseline authenticated testing. - Apply provided username and password wordlists for brute-forcing when potential enumeration endpoints are identified.
- Utilize the standard test credentials (
3. Targeted Scanning: The Speed of a Professional
Time is your most significant adversary during the BSCP exam. To succeed within the 2-hour limit, integrate Burp Scanner as a surgical tool during manual testing.
[!IMPORTANT] The Hybrid Approach In the BSCP context, automated scanning is not a replacement for expertise—it is a force multiplier. Targeted scanning rapidly clears low-hanging fruit and common injection points, preserving mental bandwidth for multi-step exploits and broken logic flaws requiring human intuition.
4. Critical Skills Deep-Dive: Essential Prep Labs
Mastery of these specific labs reinforces the high-impact primitives tested on the certification:
| Vulnerability / Lab Name | The "Core Skill" Developed |
|---|---|
| Exploiting XSS to steal cookies | Mastery of cross-user attacks and session hijacking techniques. |
| Blind SQL injection with OOB exfiltration | Advanced data extraction using Out-of-Band (OAST) channels via Burp Collaborator. |
| SSRF with blacklist-based input filter | Developing a defense-evasion mindset against restrictive security filters. |
| Forced OAuth profile linking | Identifying and exploiting fundamental logic flaws in authentication flows. |
| Brute-forcing a stay-logged-in cookie | Understanding and attacking persistent session and "remember me" token generation. |
| HTTP request smuggling to capture requests | Expert-level traffic manipulation to intercept sensitive user data across desynchronized servers. |
| SQL injection with bypass via XML encoding | Utilizing encoding strategies to evade WAFs and input filters. |
5. The Final Rehearsal: Practice Exam Simulation
The Practice Exam is your final gate: a two-hour simulation featuring one complex, vulnerable application.
- High-Fidelity Diagnostic: Passing demonstrates both speed and depth. Failing is a clear signal to return to Mystery Labs or revisit the Step 2 prep labs.
- Study Official Intel: Read and internalize the PortSwigger Exam Hints and Guidance.
- The Readiness Rule: Never purchase the BSCP exam voucher until you can consistently pass the Practice Exam within the 120-minute window.
6. Final Readiness Checklist
- Completed Curriculum: Finished all Apprentice and Practitioner labs.
- Mystery Lab Proficiency: Solved 5 randomized Practitioner-level Mystery Labs consecutively without assistance.
- Scanning Integration: Completed the "Targeted Scanning" workflow to accelerate manual discovery.
- Exploitation Depth: Mastered all core deep-dive prep labs (XSS, SQLi, SSRF, OAuth, Smuggling, File Uploads).
- Simulation Mastery: Passed the two-hour Practice Exam under strict timing.
- Briefing Review: Read and internalized the official exam hints and guidance.
🔗 PortSwigger Lab Walkthroughs
Below is a running log of my progress through the PortSwigger Web Security Academy labs. I will be updating this list with detailed write-ups for each lab as I complete them on my journey to passing the BSCP.
- Walkthroughs coming soon...